Authentication
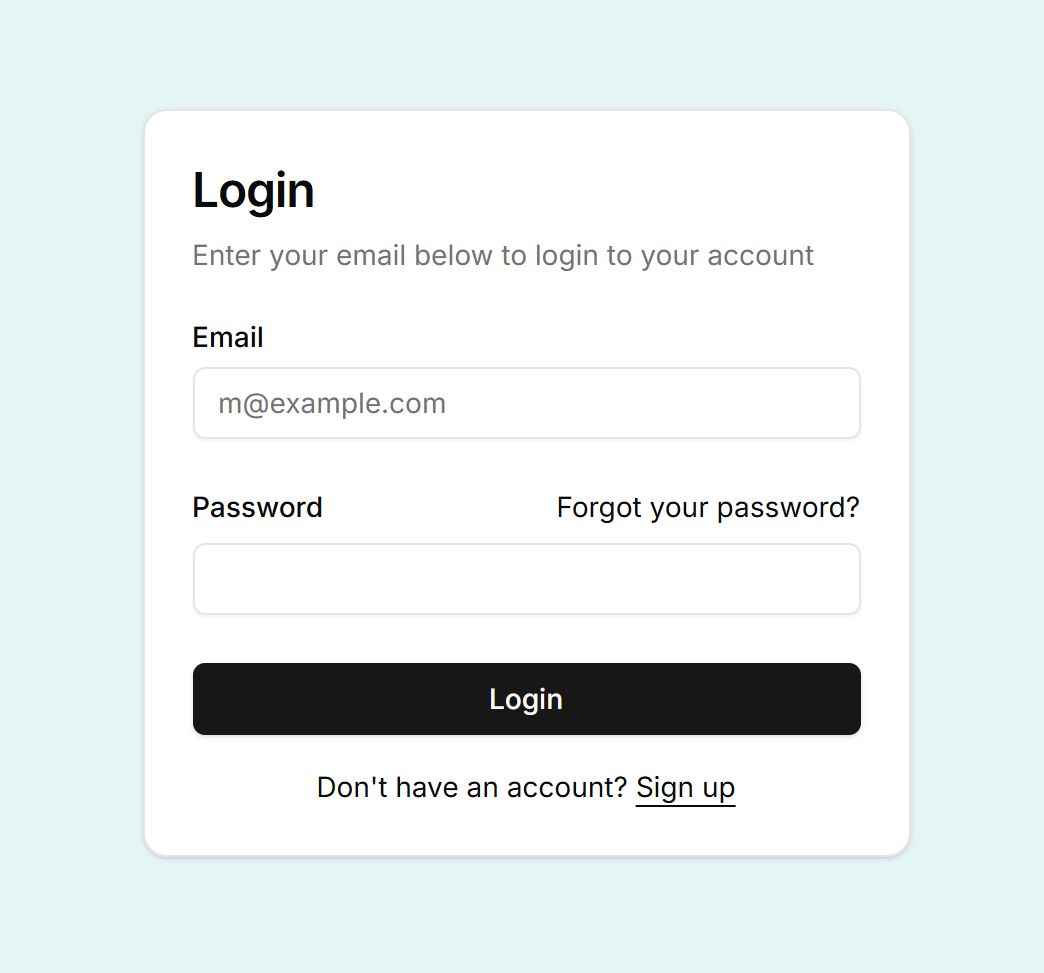
The first thing you need to do with your new authentication setup is to create a login for yourself, such that you can get access to your project again. Click on the Sign up link at the bottom of the login screen.
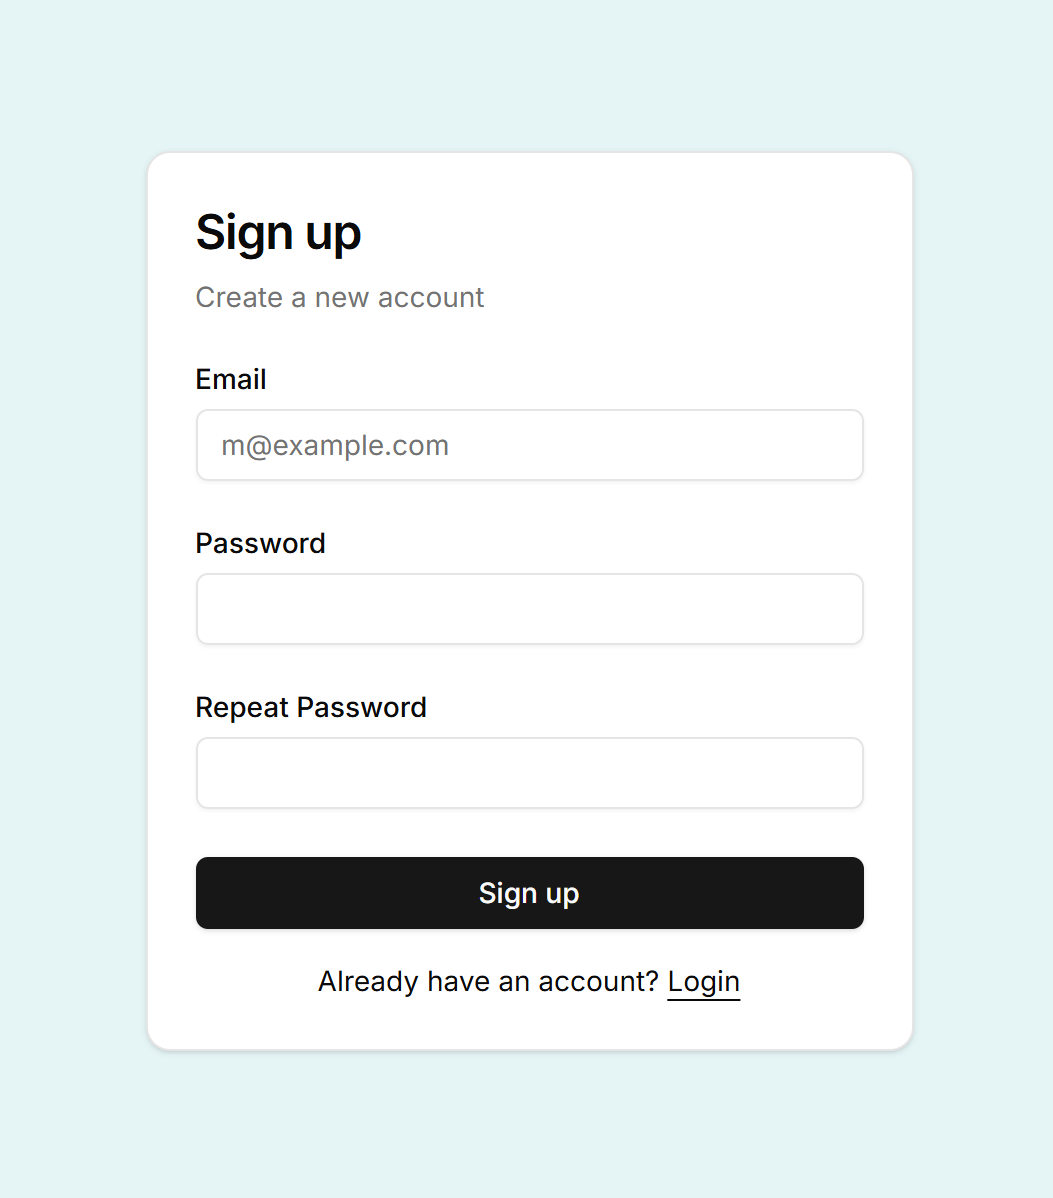
Enter your email, pick a password and repeat it, and click Sign up.
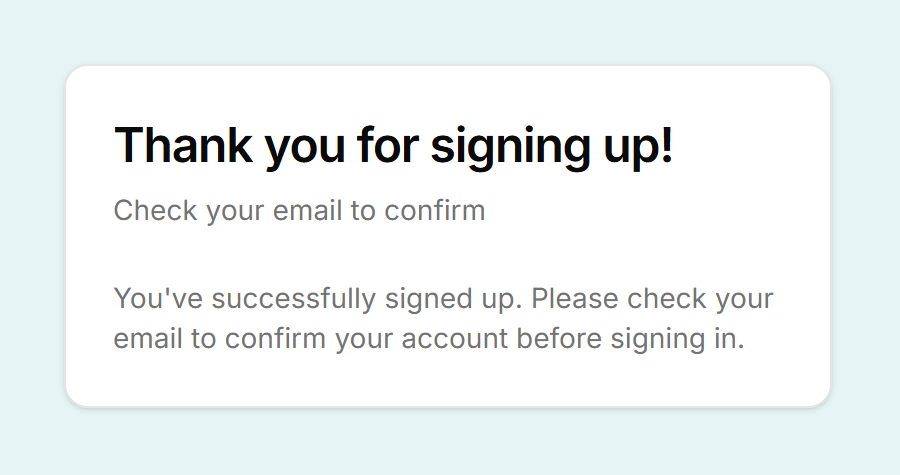
Then you see this message, asking you to confirm your mail address:
The mail you receive to confirm your mail address, looks like this:
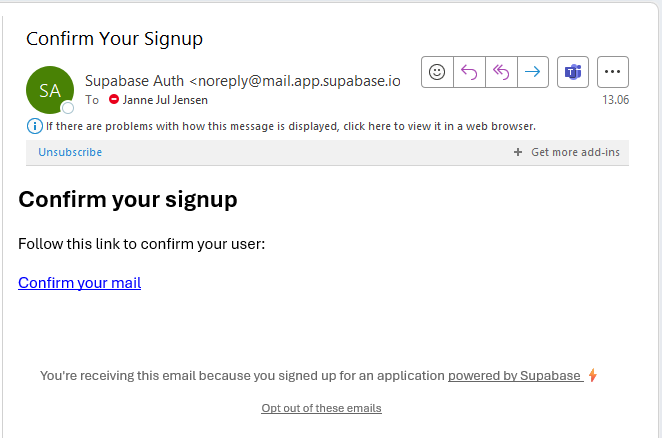
Go ahead and click the link, but be prepared that it does not return you to Henosia. It will open the page http://localhost:3000 and this will look like a page unable to load. The confirmation worked as it should, however, and when you go back to Henosia, you are now able to login with your credentials.
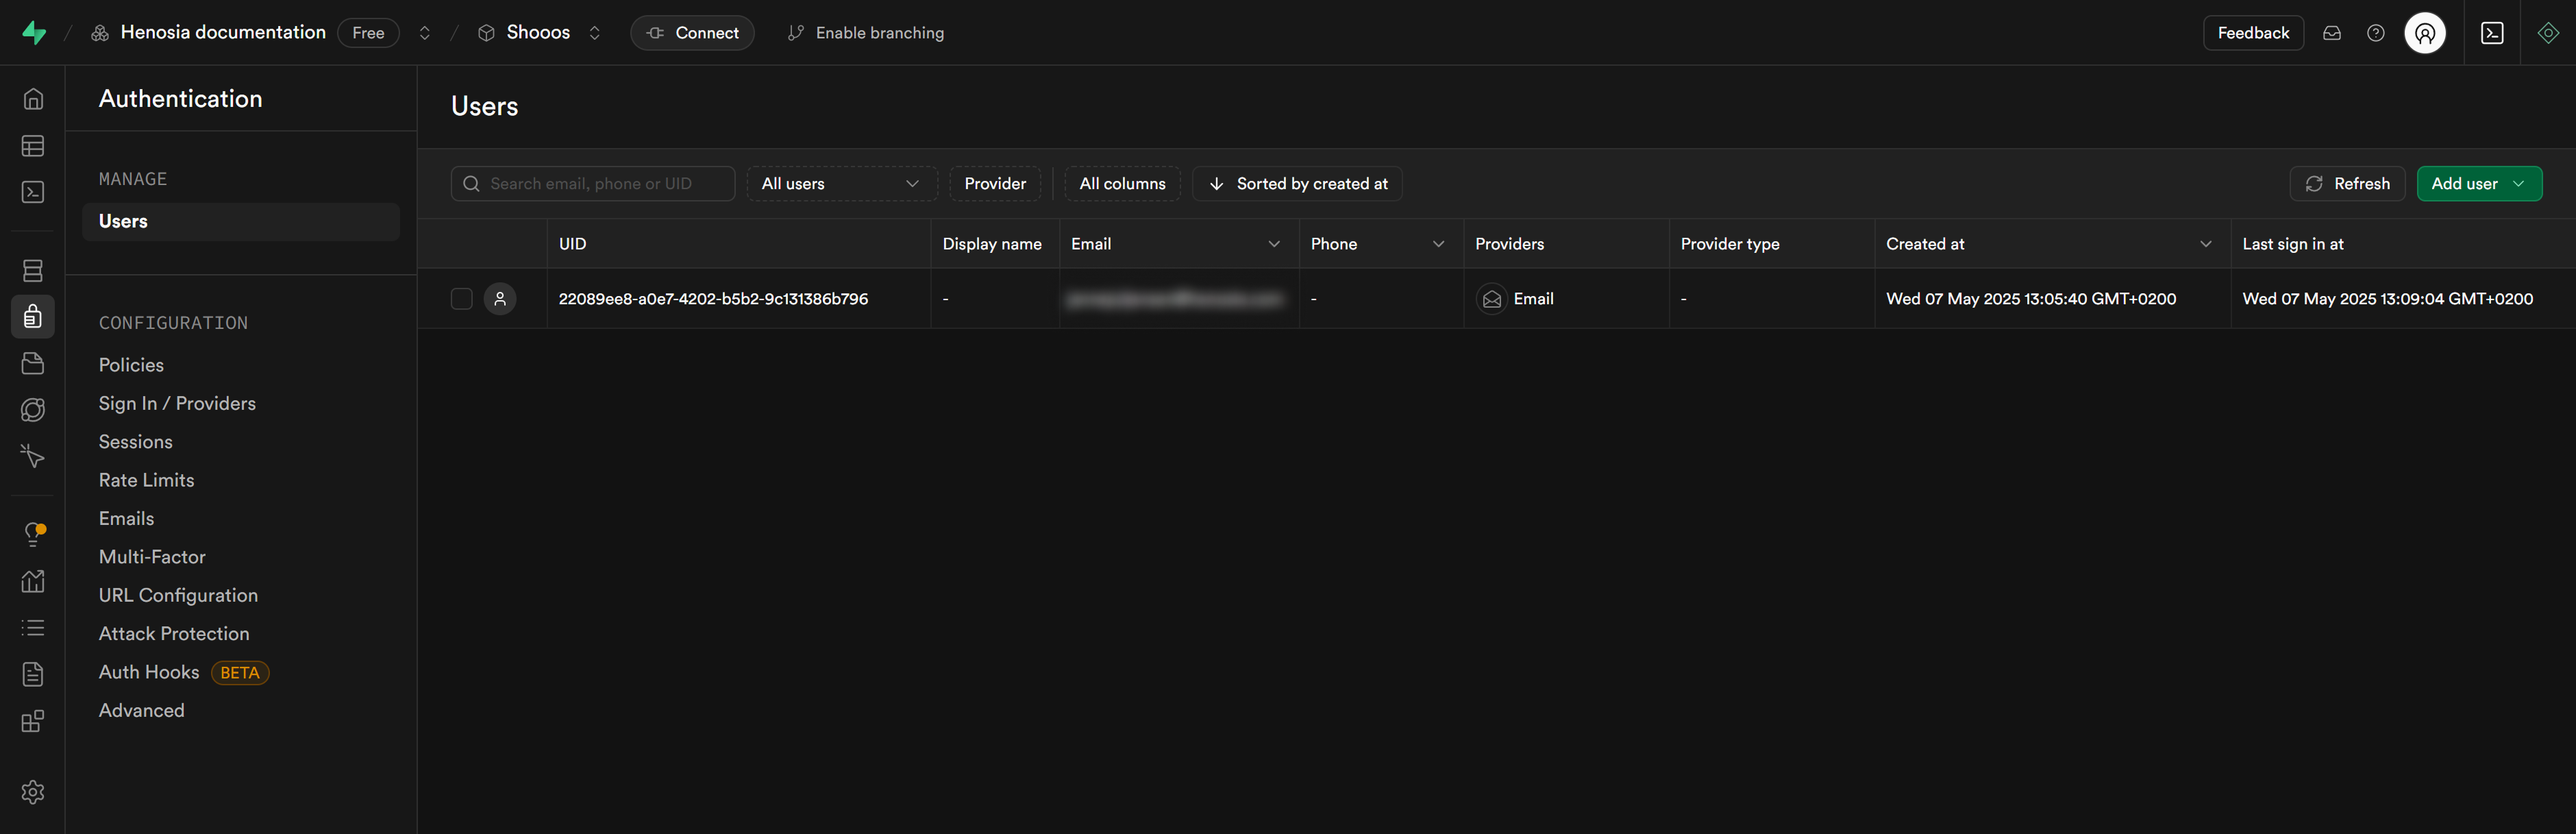
If you visit Supabase and look under Authentication, you should be able to see yourself as an entry in the list of people with credentials for your project. as other people sign up, they will also show up here.
Once you're logged in, you land on a page called /protected that looks like this:
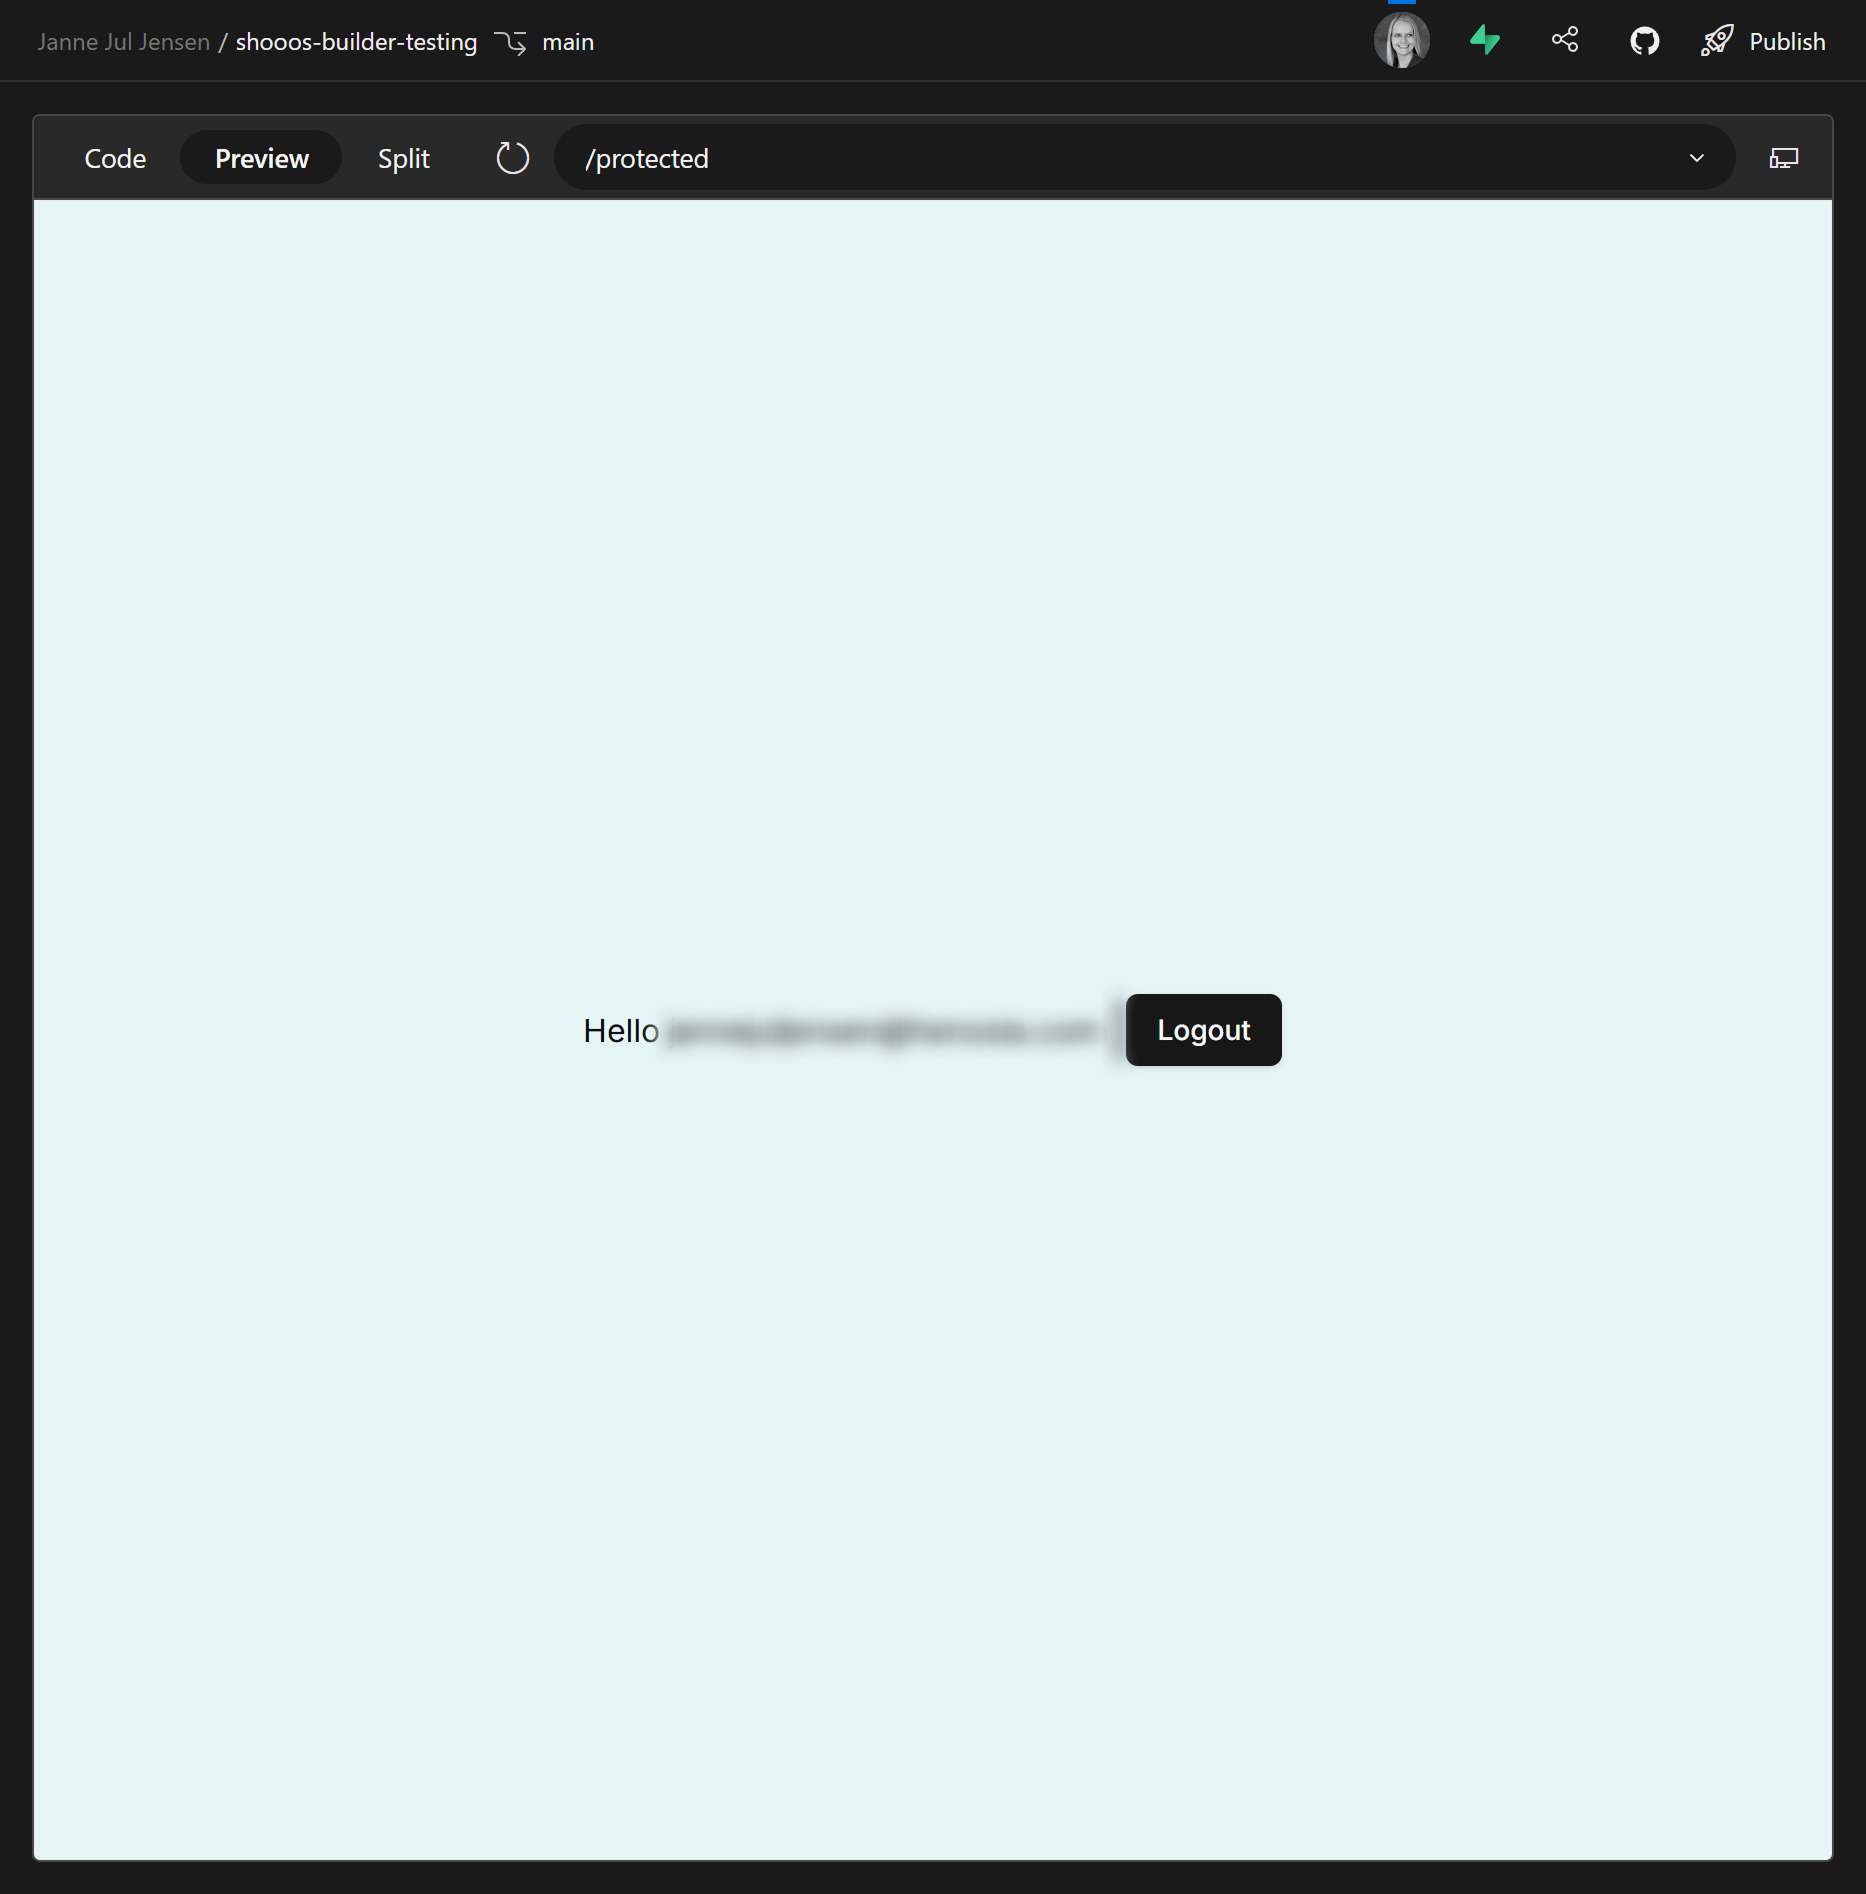
This is most likely not where you want your users to land after login, but you can fix that with a prompt along the lines of:
After login the user should land on the front page, not on the page /protected.
So far your product may also have had hardcoded data about who was logged in, while there was no backend connected. You want that to be changed to use Supabase and reflect who is actually logged in. Tell Henosia the result you want, for example:
Replace the mock user data, such as the name "John", with the details of the person logged in via Supabase, everywhere the site shows them.
Then go through your pages in the preview, such as the account page, and tell Henosia what else you want fixed. Read more about writing prompts in Tips & Tricks
Similarly, there may be pages to which you don't require the user to be logged in and others where you do. For instance, in our shoe shop, we want people to be able to browse the shoes, put them in the basket etc. without being logged in. But account, previous orders, check out flow, etc. we want them logged in.
This, and any other tweaks you want to make to how authentication works can now be done via prompting.